
New Delhi:
Nicholas Butts, Director of AI and Cybersecurity Policy at Microsoft, on Friday listed three recent threats to India specifically, noting that it’s the seventh most targeted country in the world when it comes to cybersecurity, and the third most targeted in Asia.
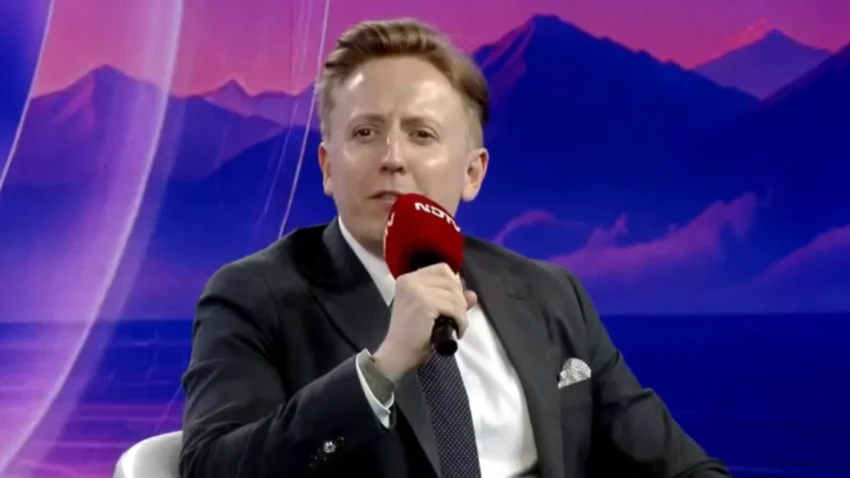
Speaking at the NDTV World Summit 2026 in New Delhi, Butts said, “We get about 165 trillion telemetry signals that we process every day. We screen about 5 billion emails every day. We block about 5 million net-new malware files every day. We have quite a unique vantage point on some of this.”
“What we’re seeing is not about potential doom and gloom in 10 years but about very real security threats right here today,” he added, using a “leaky roof” analogy.
“The threat is very real to India,” he stressed.
Asked about state actors such as China, North Korea, or even Pakistan, Butts listed examples of some recent threats. “A threat actor that we tracked is ‘Storm 3168′, sometimes called Jadepuffer. It’s a ransomware organisation that’s based out of China, essentially using AI agents to conduct ransomware attacks against customers all over the world,” he listed.
As a second example, he cited “Russian and Chinese state-sponsored actors using agents as part of their espionage campaign”. “As late as yesterday (October 22), Microsoft published a new threat intel report about a new state actor that we track as ‘Storm 0940′, a Chinese state-sponsored linked actor mainly targeting data theft and espionage purposes,” he explained.
As a third threat, he said cybercriminals are becoming a lot more capable with AI. “In February, there was a new threat actor that was called ‘EvilTokens’ that we began to track. It’s essentially two individuals that were able to vibe-code using open-source models and closed-source models. It was a totally autonomous criminal infrastructure selling access to this for $1,500, with a $500 subscription a month for first-time buyers. You would get access to a lot of tools that you were able to use for expensive cyber purposes. It impacted more than 10,000 organisations across 120 countries.”